Threat intelligence · Offensive security · Microsoft security Analyst-led engagements

Know your exposure.
Fix it before it is used.

Kage Security Lab helps organisations see what an attacker can see: exposed systems, weak identity controls and leaked credentials. We monitor the sources adversaries use, test your defences against current techniques, and help you close the gaps that matter most.

Free browser tools
24No sign-up, no tracking
Tool queries stored
0Everything runs client-side
Security services
9Intel · Testing · Microsoft
Depth layers covered
3Light · Shade · Shadow
Example signals
  • Credential combo list naming finance-sector domains posted to a closed forum
  • AiTM phishing kit targeting Microsoft 365 sign-in observed in the wild
  • Look-alike domain registered 48h before a payroll-themed campaign
  • Infostealer logs with session cookies for SaaS admin portals offered for sale
  • Ransomware affiliate recruiting initial access brokers for healthcare targets
  • OAuth consent phishing app requesting Mail.ReadWrite reported
  • Exposed .env file with cloud keys found on a forgotten staging host

FIG. 02 — Depth

Light. Shade. Shadow.

Three layers of exposure. We cover all of them.

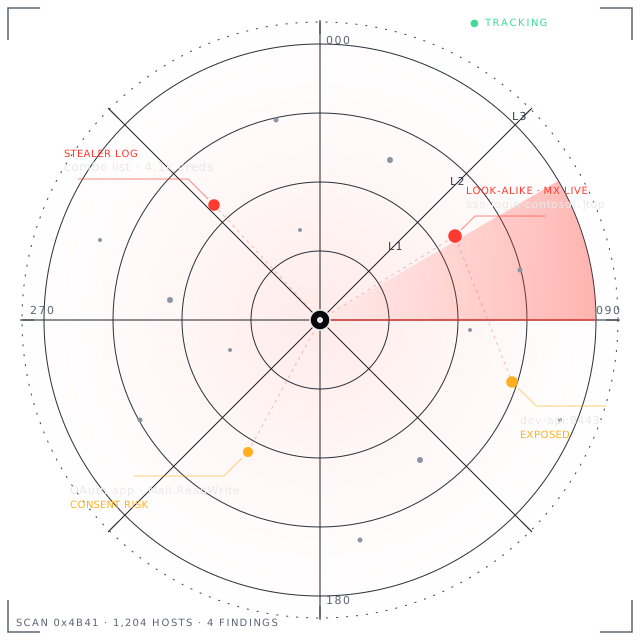
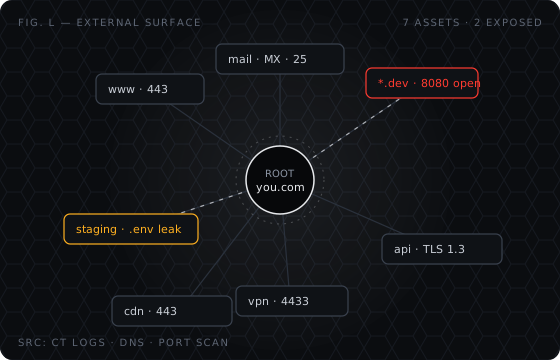
Light layer illustration

00 — External surface

Light Everything an attacker can see without asking.

We map your internet-facing footprint the way reconnaissance tooling does: domains, subdomains, certificates, exposed services, look-alike domains, fake apps and leaked documents.

  • Attack surface & certificate transparency mapping
  • Brand impersonation & typosquat monitoring
  • Leaked code, keys and documents
Shade layer illustration

01 — Identity & cloud

Shade The layer most breaches actually go through.

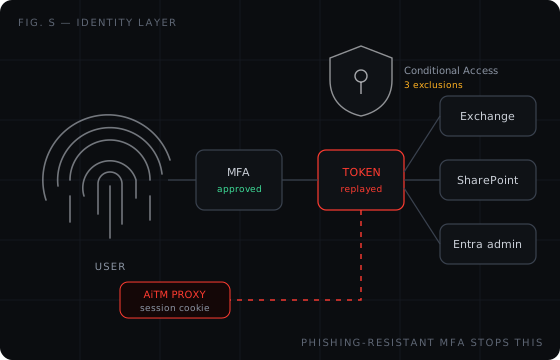
Identity is the new perimeter. We assess Microsoft Entra ID, Microsoft 365, Conditional Access and SaaS tenants for the misconfigurations that turn one phished user into a tenant-wide incident.

  • Entra ID & Conditional Access review
  • Microsoft 365 / Exchange / SharePoint hardening
  • OAuth app & consent abuse detection
Shadow layer illustration

02 — Criminal underground

Shadow Where your data is priced and traded.

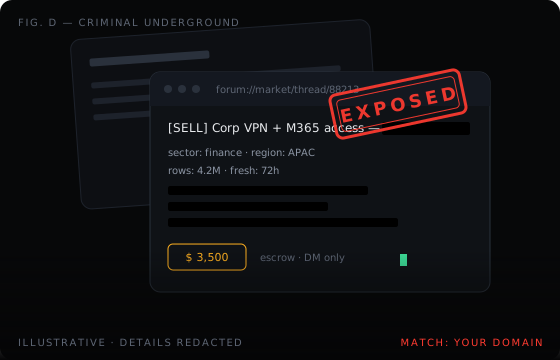
Analysts track forums, marketplaces, stealer-log channels and ransomware leak sites for your domains, executives and suppliers, then work the finding through to remediation or takedown.

  • Dark web & stealer-log monitoring
  • Threat actor profiling for your sector
  • Takedown & exposure response

FIG. 03 — Services

Watch the underground. Test the perimeter.

Most providers either watch or test. We do both, and each side informs the other.

Threat Intelligence Threat Intelligence & Dark Web Monitoring Continuous monitoring of forums, marketplaces, stealer-log channels and ransomware leak sites for your domains, people and suppliers. Learn more Threat Intelligence Brand & Domain Protection Detection and takedown of look-alike domains, fake social profiles, rogue mobile apps and phishing pages that impersonate your brand. Learn more Security Operations Vulnerability Assessment & Penetration Testing Manual, standards-aligned testing of web applications, APIs, external and internal networks, cloud and mobile apps. Learn more Security Operations Red Team Operations Objective-based adversary emulation built from the threat actors and TTPs actively targeting your sector. Learn more Security Operations Incident Response & Compromise Assessment Rapid investigation of suspected compromise across endpoints, identity and Microsoft 365, with containment guidance from first call. Learn more Microsoft Security Microsoft 365 & Entra ID Security Assessment A deep review of your Microsoft cloud tenant (identity, Conditional Access, privileged roles, OAuth apps, Exchange and SharePoint) and how it works with the rest of your security stack, Microsoft or not. Learn more Microsoft Security Entra ID & Conditional Access Hardening Design and roll out Conditional Access, phishing-resistant MFA and privileged access controls that stop account takeover without locking users out. Learn more Microsoft Security Microsoft Defender XDR Deployment & Tuning Get full value from the Defender licences you already own: onboarding, attack surface reduction, automated response and alert tuning across endpoint, identity, email and cloud apps. Learn more Microsoft Security Microsoft Sentinel & Managed Detection Deploy Microsoft Sentinel with the right data, detections and automation, or let our analysts watch it for you around the clock. Learn more
01

Analysts, not alert floods

Every finding is human-verified and arrives with context, impact and a recommended action.

02

Intel shapes the testing

Red team scope is built from the actors and TTPs actually targeting your sector this quarter.

03

Microsoft cloud depth

Purpose-built tooling for Entra ID and Microsoft 365 assessments, maintained in-house.

04

Closed-loop response

We do not stop at the report. Findings are tracked through remediation, takedown or confirmed removal.

FIG. 04 — Platform

Kage Security Toolkit

Our in-house Microsoft 365 and Entra assessment platform. Clients get continuous posture scans, Conditional Access analysis, Zero Trust scoring and guided remediation, all under their own tenant consent.

Client sign-in About the assessment

FIG. 05 — Risk

Exposure has a price tag.

Regulators expect you to know what is exposed. We assess against the frameworks your auditors use.

Assessments aligned to

  • ISO/IEC 27001
  • SOC 2
  • PCI DSS v4.0
  • NIST CSF 2.0
  • CIS Controls v8
  • MITRE ATT&CK
JurisdictionLawMaximum penalty
European UnionGDPRUp to €20M or 4% of global annual turnover
California, USCCPA / CPRAPer-violation fines; higher for intentional violations
United KingdomUK GDPRUp to £17.5M or 4% of global annual turnover
SingaporePDPAUp to 10% of local turnover or S$1M
ChinaPIPLUp to ¥50M or 5% of prior-year turnover
IndiaDPDP ActUp to ₹250 crore per instance

Summary only, not legal advice. Penalty ceilings vary by violation type and change over time.

See your organisation the way attackers do.

Book a scoping call. We will show you what is visible about your organisation today and what to fix first.

Book a scoping call Try the free tools